Publisher key
Every publisher on the marketplace (an organization, or an account publishing in its own name) has a publisher key. Each package file you download, or that a connected platform fetches, is signed with the key of the package’s publisher.
Where to find it
Section titled “Where to find it”On the Profile tab of an organization space, the Publisher key card shows:
- Fingerprint: a short identifier of the key, 16 hexadecimal characters such as
3f9c2a7be1d04c58; - Created: when the key was made.
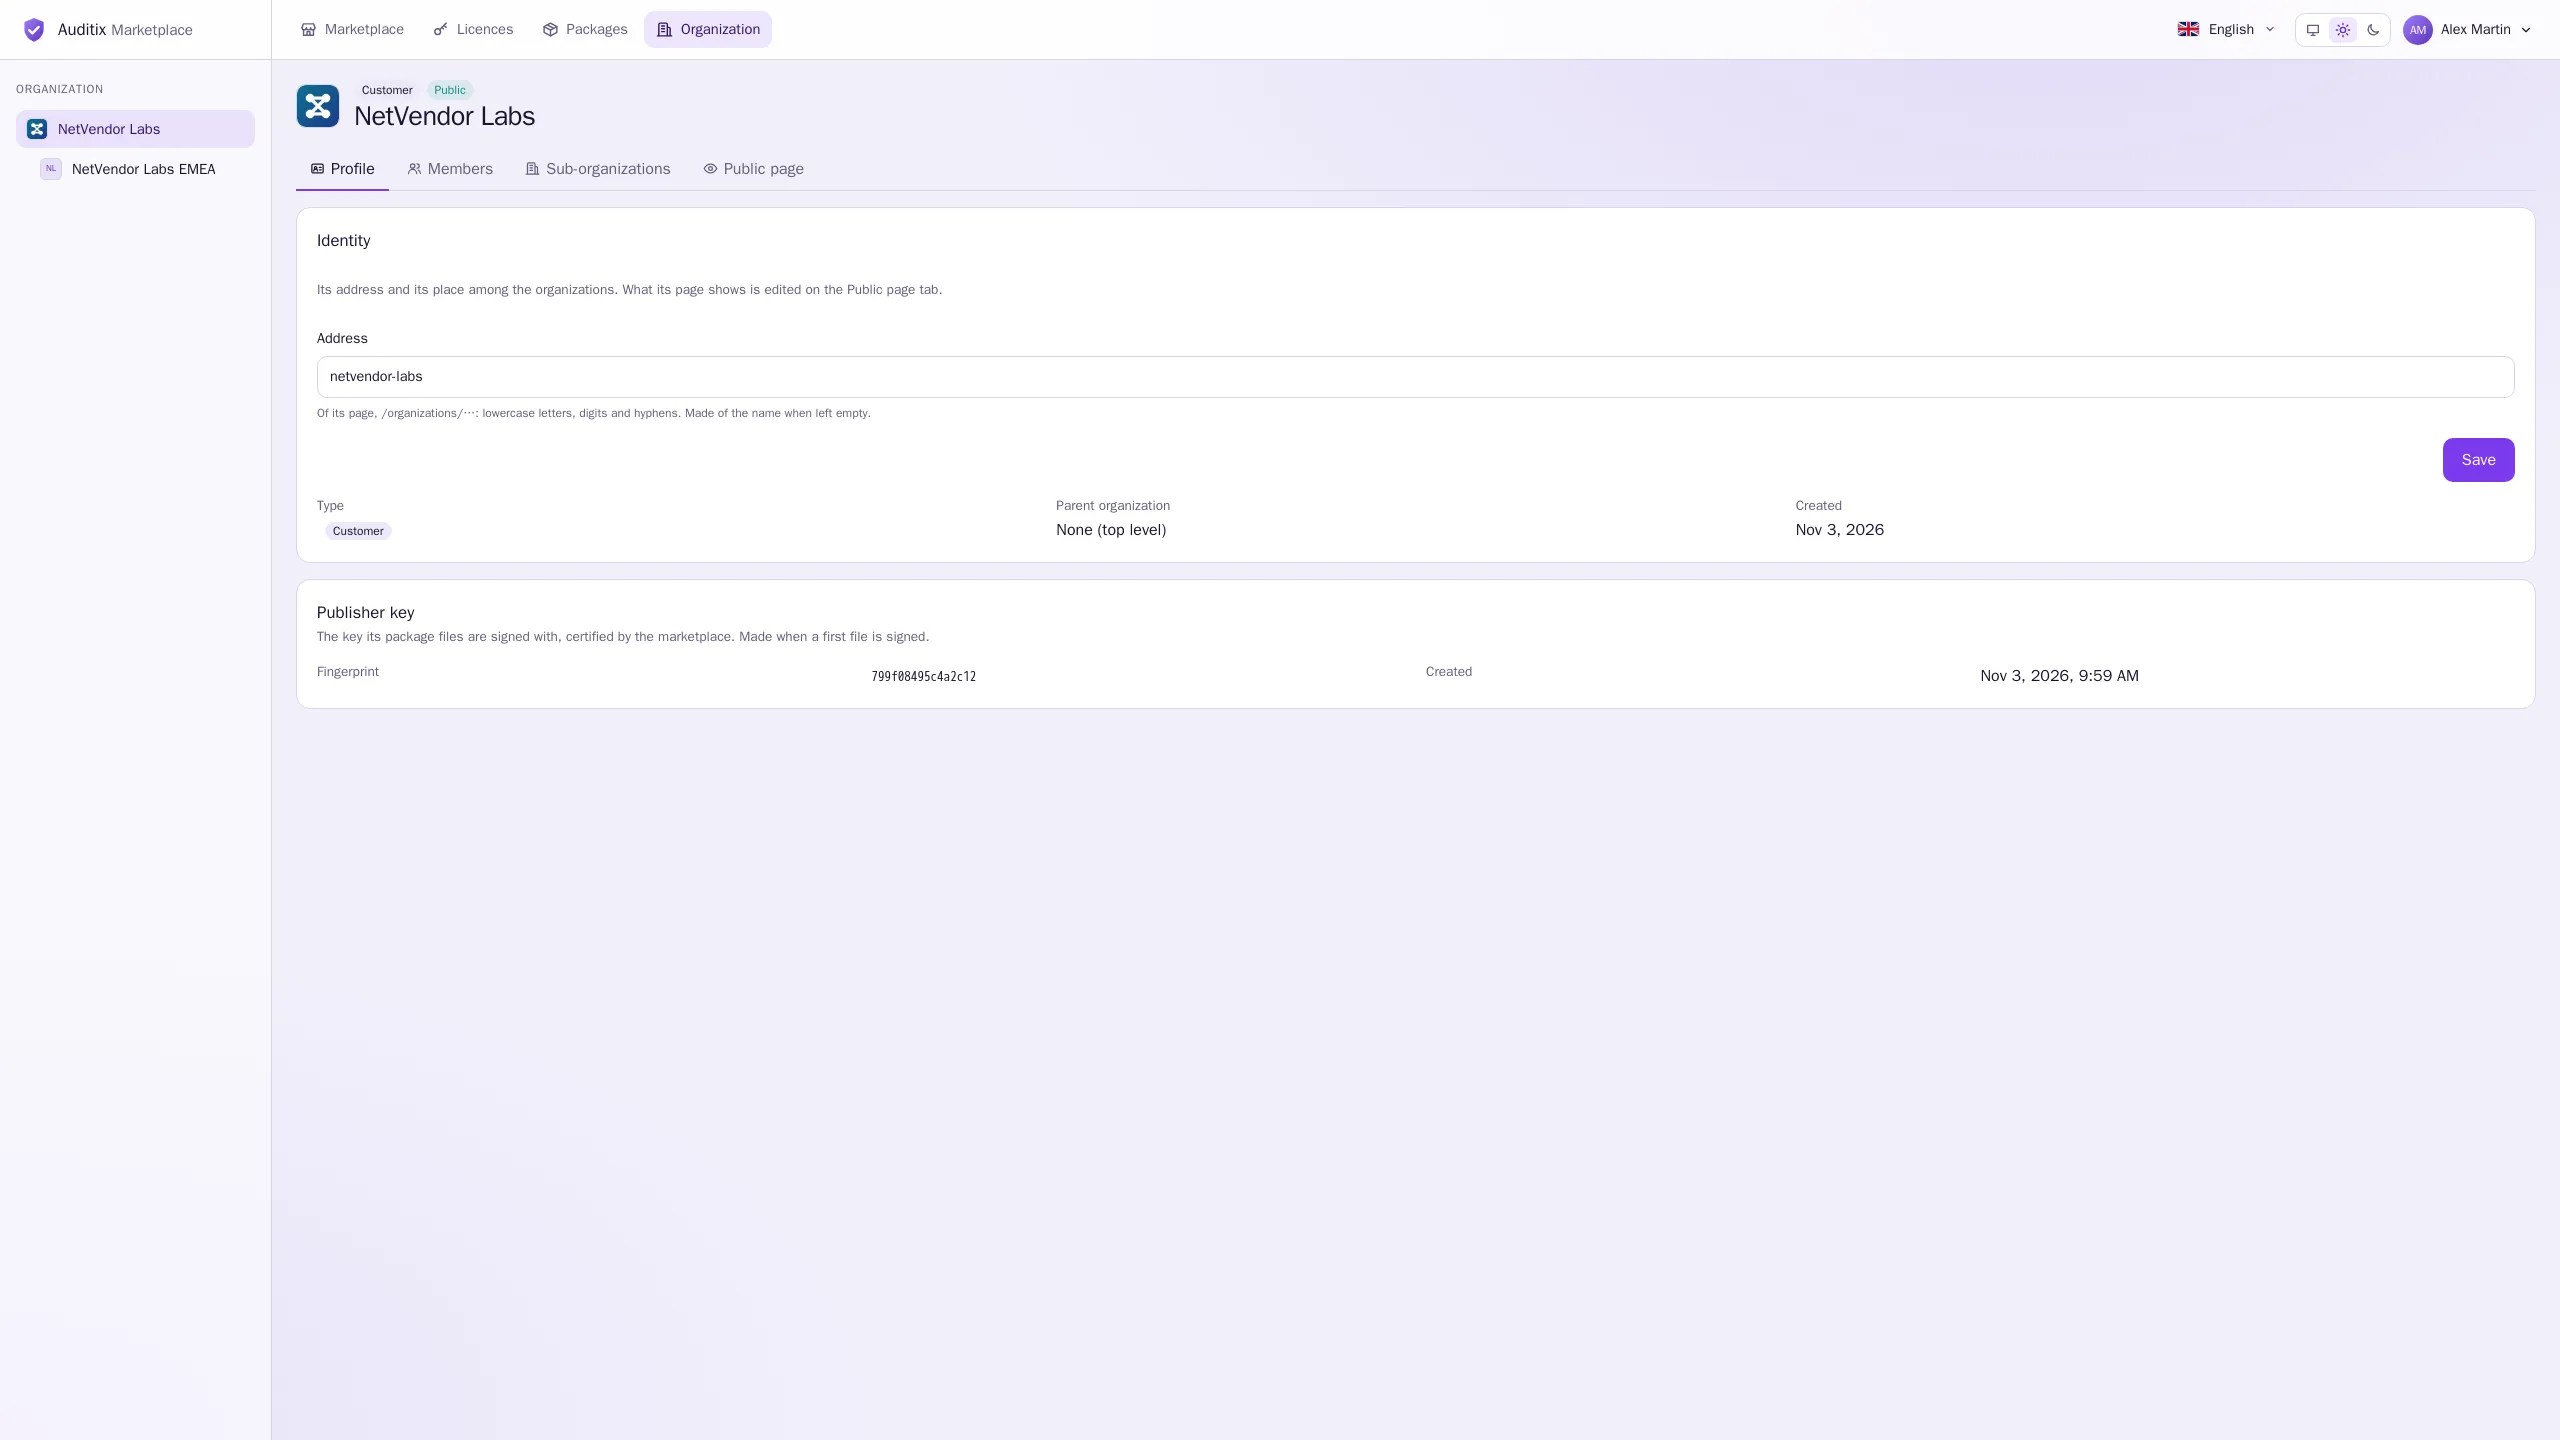
Before the organization’s first file is signed, the card says No key yet: it is made when a first file is signed. There is nothing to set up: the marketplace makes the key and keeps it. Its private part is never shown or downloadable.
What the signature guarantees
Section titled “What the signature guarantees”The marketplace vouches for each publisher key with a certificate, carried in every package file. When a platform imports a file, it checks:
- that the certificate was issued by the Auditix marketplace;
- that the file is signed by the key named in that certificate, so it was not altered since it was published;
- that the publisher written in the package is the one the certificate names.
A file that fails any of these checks is refused (for example This package is not signed by its publisher). A valid one is shown on the platform as Signed by <publisher> (<handle>), certified by the Auditix marketplace, with the package and publisher logos. See Signatures on the platform side.
Signature and certification are different
Section titled “Signature and certification are different”| Means | |
|---|---|
| Signature (every package) | The file really comes from this publisher, unchanged, through the marketplace. It says nothing about the quality of the content. |
| Published by Auditix | The publisher is the Auditix team. |
| Certified by the vendor | The vendor whose equipment the package covers (a Vendor organization) has certified it. |
| Community | Signed by its publisher, but neither published by Auditix nor certified by a vendor: review it before using it in production. |
Key rotation
Section titled “Key rotation”If you believe your key is compromised, contact the Auditix team: they replace it with a new one. Files signed from then on use the new key; files downloaded before stay valid, because their certificate is still signed by the marketplace.